The Card
Holmes receives a breadcrumb from Dr. Nicole Vale - fragments from a string of cyber incidents across Cogwork-1. Each lead ends the same way: a digital calling card signed JM.
We’re given a couple log files with a docker. The logs are access.log, application.log and waf.log. We need to analyze the log files in order to get the answer for each question.
1. Analyze the provided logs and identify what is the first User-Agent used by the attacker against Nicole Vale’s honeypot. (string)
We can get the answer by checking the couple first lines of access.log.
Based on the log files, we know that the User-Agent that is used by the attacker is Lilnunc/4A4D - SpecterEye
2. It appears the threat actor deployed a web shell after bypassing the WAF. What is the file name? (filename.ext)
Based on the question, we can reduce our scope to analyzing only the WAF logs (since the question mentioned bypassing the WAF).
From the details of the log file, we can see that there’s a rule named WEBSHELL_EXECUTION and the Action is BYPASS from that message we can check the filename which is temp_4A4D.php
3. The threat actor also managed to exfiltrate some data. What is the name of the database that was exfiltrated? (filename.ext)
We can find the name of the database near the WEBSHELL_EXECUTION rule. The rule name is DATABASE_DOWNLOAD and the filename is database_dump_4A4D.sql
4. During the attack, a seemingly meaningless string seems to be recurring. Which one is it? (string)
From the previous questions, we always find 4A4D string and I suspect that 4A4D is the answer and it’s correct.
To solve this, we can check each campaign whether it mentions 4A4D or not. The campaigns are
- Transport Chaos
- Operation Neural Storm
- Civic Disruption
- Bio-Breach
- Quantum Heist
and the answer is 5 campaigns
To answer this question, we can just count the total number of malware and tools that are linked to each campaigns
- Transport Chaos (1 Malware)
- Operation Neural Storm (1 Tool and 1 Malware)
- Civic Disruption (1 Tool and 1 Malware)
- Bio-Breach (1 Tool and 1 Malware)
- Quantum Heist (1 Tool and 1 Malware)
and the answer is 9
7. It appears that the threat actor has always used the same malware in their campaigns. What is its SHA-256 hash? (sha-256 hash)
To solve this, we can check each indicator that is linked directly to the malware and find the hash that is used multiple times.
The answer is 7477c4f5e6d7c8b9a0f1e2d3c4b5a6f7e8d9c0b1a2f3e4d5c6b7a8f9e0d17477
To solve this question, we can search the hash using the platform on the second docker ip:port address and find the IP address
The answer is 74.77.74.77
9. What is the full path of the file that the malware created to ensure its persistence on systems? (/path/filename.ext)
To find the file, we can view the details using the same platform from question number 8 and find the path.
The answer is /opt/lilnunc/implant/4a4d_persistence.sh
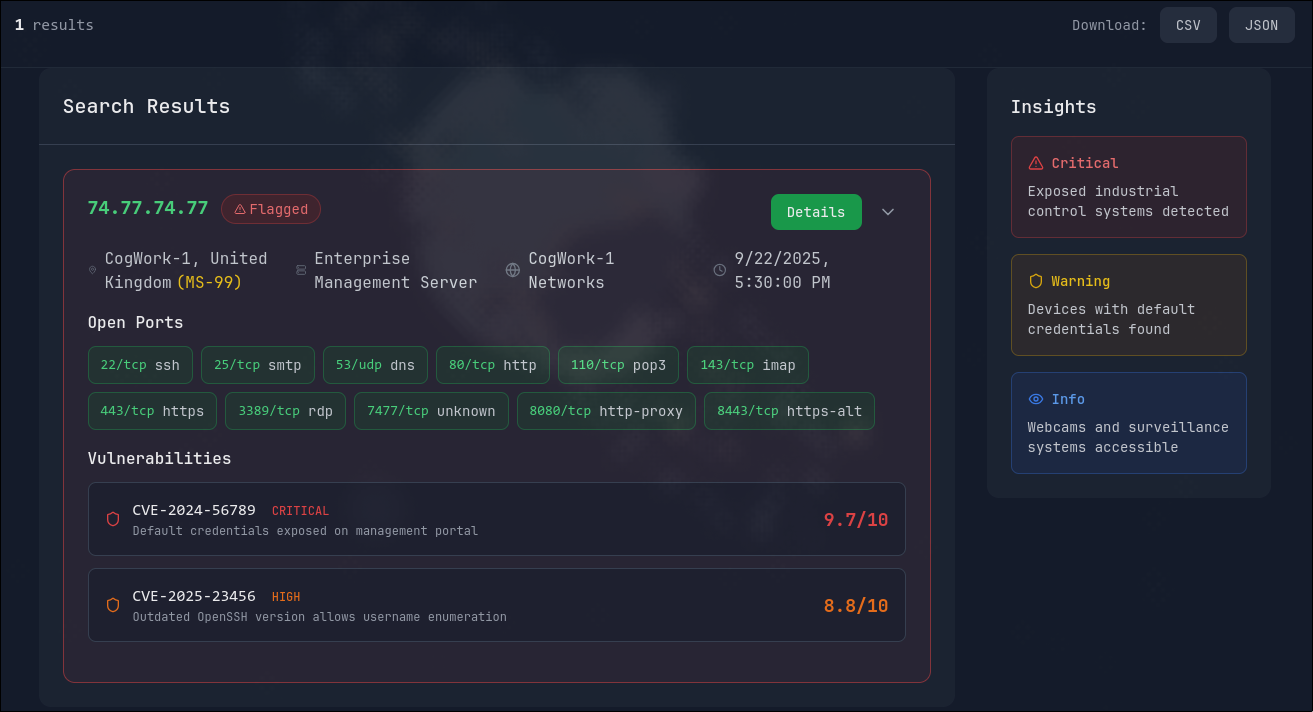
To solve this, we can use the third ip:port from the docker and search the 74.77.74.77 on the platform.
Based on the search, the number of open ports are 11
11. Which organization does the previously identified IP belong to? (string)
To solve this question, we can click the details button and find the name of the organization
The answer is SenseShield MSP
12. One of the exposed services displays a banner containing a cryptic message. What is it? (string)
To solve this question, we can check the Services tab and find the unique banner
The answer is He's a ghost I carry, not to haunt me, but to hold me together - NULLINC REVENGELast modified on September 29, 2026